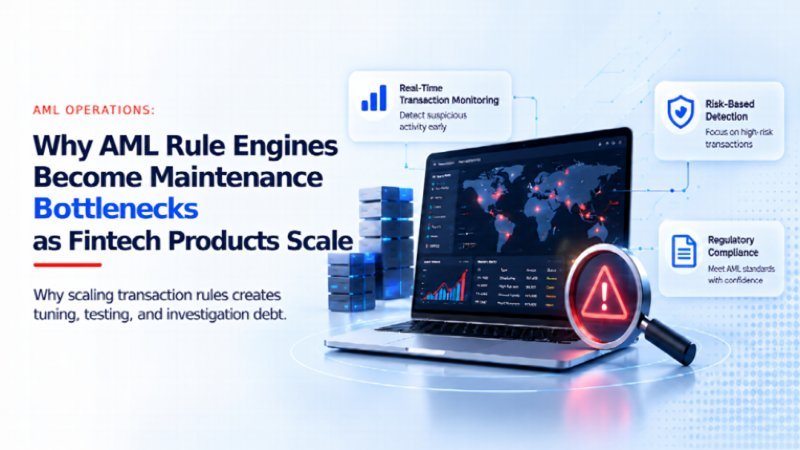
AML rule engines are often manageable when a fintech product is small. A limited set of transaction types, customer profiles, and payment flows can be monitored with thresholds and scenario-based rules that are relatively easy to understand.
That changes as the product grows. New payment methods, business accounts, lending products, international transfers, and partner integrations introduce new patterns of legitimate behavior alongside new risk scenarios.
The problem is not simply that more transactions need to be screened. Each product variation can create additional rules, exceptions, thresholds, data dependencies, and investigation requirements. Over time, the rule engine can become one of the slowest parts of the compliance stack to change.
Why AML Rule Engines Become Harder to Maintain at Scale
Rule-based monitoring works because its logic is explicit. A fintech can flag transactions above a threshold, repeated transfers within a short period, activity involving higher-risk geographies, or behavior that differs from an expected customer profile.
That transparency is useful. Compliance teams can understand why an alert was created, and investigators can trace it back to a specific condition.
Scale makes those conditions less universal. A $5,000 transfer may be unusual for a new consumer wallet but routine for a business account. Ten transfers in an hour could indicate suspicious velocity in one product while reflecting ordinary merchant activity in another.
1. Rule Volume Grows With Product Complexity
Fintech products rarely scale by processing more of the same activity. They add services.
A wallet may expand into merchant payments, remittances, virtual cards, rewards, lending, or business accounts. Each service changes what normal behavior looks like and introduces new monitoring scenarios.
Teams respond by creating narrower conditions around account type, customer risk, geography, transaction channel, payment method, and historical behavior. One rule gradually becomes several versions, each with its own testing, tuning, documentation, and review cycle.
The result is not only a larger rule library. It is a larger maintenance surface. Each rule has assumptions that can become outdated as customer behavior, product design, and transaction patterns change.
2. False Positives Become an Operations Problem
False positives are not only a detection-quality issue. They consume investigator capacity.
Every alert can require a review of transaction history, customer information, previous alerts, account relationships, and risk scores. If a rule produces large numbers of low-value alerts, review queues grow and investigators spend less time on complex cases.
Adding more investigators can help absorb the volume, but it does not correct the monitoring problem itself. If transaction volumes continue to rise while the same rules produce the same proportion of unnecessary alerts, operating costs rise with them.
This is why AML software development has to account for the complete investigation workflow rather than only the logic that generates an alert. A monitoring system is useful only when its alerts can be reviewed meaningfully at scale.
3. Exceptions Turn Into Maintenance Debt
Rules also become harder to maintain because exceptions accumulate.
A scenario may begin as a simple condition: flag transactions that meet threshold X.
Later, the same condition may need exclusions for a customer segment, product type, payment channel, geography, review status, or behavioral pattern.
Each exception may be reasonable on its own. The problem appears when business and product logic starts living inside the monitoring layer.
A change to one product can then require updates across several rules because each contains its own interpretation of that product. Teams are no longer maintaining only risk scenarios. They are also maintaining an increasingly complicated representation of how the fintech product operates.
4. Testing Changes Gets More Expensive
A rule change cannot be evaluated only by confirming that the code runs.
Teams need to understand what would happen if the revised rule were applied to historical activity. Would alert volume fall? Would false positives decline without removing useful detections? Could one customer group be affected more than another?
Answering those questions requires historical datasets, replay testing, rule versioning, measurable outcomes, and clear approval paths.
Dependencies make the process harder because one risk score or shared data field may influence several monitoring scenarios. A change that appears isolated may therefore alter alert behavior elsewhere in the system.
As the rule library expands, testing becomes less about validating one condition and more about understanding its effect on a connected monitoring environment.
5. Product and Compliance Teams Move at Different Speeds
Fintech products can change quickly. AML controls often need a different change process.
A new feature may require revised monitoring scenarios, additional data capture, investigator guidance, testing, documentation, and approval. That creates a coordination challenge between product, engineering, risk, and compliance teams.
The same applies when companies use fintech app development services. AML requirements should not be treated as a final integration after the product architecture is already decided.
Audit trails, customer identity data, transaction events, permissions, and monitoring inputs are architectural concerns too. Designing those foundations early is considerably easier than reconstructing them after transaction volumes and compliance requirements have expanded.
Building AML Monitoring That Scales Better
The answer is not to remove rules. Explicit conditions remain useful when a risk scenario can be clearly defined and investigators need to understand why activity was flagged.
A more scalable approach is to stop making individual rules responsible for every piece of customer and product context.
Reusable risk signals can be calculated centrally. Customer behavior can be compared with relevant peer groups. Common identity, transaction, and account information can be made available across multiple monitoring scenarios instead of being reconstructed inside each rule.
Analytics and behavioral monitoring can also help identify patterns that static thresholds may struggle to capture. These capabilities do not necessarily replace deterministic rules. Instead, they can help teams determine which situations are best handled by explicit conditions and which require broader behavioral context.
Governance matters just as much as technology.
Rules should have clear owners, documented purposes, version histories, testing criteria, review schedules, and retirement conditions. Teams should also know when a rule no longer provides enough useful detection value to justify the investigation workload it creates.
Without a retirement process, the rule library only grows.
For fintech companies that need outside engineering support, the relevant question is therefore broader than whether a provider can build a transaction-monitoring interface. Data architecture, integrations, auditability, security, and long-term maintainability all influence whether AML controls remain workable as the underlying product scales.
5 US Product Engineering Companies Relevant to AML-Heavy Fintech Builds in 2026
Fintech companies evaluating external engineering support may need expertise beyond basic application development. Transaction monitoring can depend on data architecture, system integrations, security controls, case-management workflows, cloud infrastructure, and the ability to maintain financial products as regulatory and operational requirements evolve.
The following US-based companies provide engineering capabilities relevant to those requirements.
1. GeekyAnts
GeekyAnts is an AI-Powered Digital Product Engineering & Consulting Company. Its work spans custom software, mobile applications, AI, data, and fintech engineering. This makes it relevant when AML capabilities need to operate as part of a wider financial product architecture rather than as an isolated compliance feature.
2. INTERSOG
INTERSOG is a Chicago-based software engineering company working across custom software development, AI, data engineering, testing, and technology staffing. Its data and application engineering capabilities can be relevant when transaction-monitoring workflows need to connect with multiple product systems, internal data sources, or modernized infrastructure.
3. Taction Software LLC
Taction Software LLC provides custom software development and integration services for regulated and data-intensive environments. Its experience with secure system integrations, data exchange, and custom platforms can be relevant where AML controls depend on information flowing reliably between customer, transaction, compliance, and operational systems.
4. Unified Infotech
Unified Infotech provides custom software development, cloud engineering, application modernization, and data services from New York. These capabilities can help fintech organizations where legacy systems or fragmented data flows make transaction monitoring, rule maintenance, and compliance integrations harder to manage.
5. Virtusa
Virtusa is a Massachusetts-headquartered product and platform engineering company with experience across financial services, cloud, data, security, and digital engineering. Its enterprise engineering background can be relevant where transaction monitoring must integrate with wider banking platforms, data environments, or modernization programs.
Conclusion
AML rule engines remain useful because they provide explicit and explainable controls for known risk scenarios. The maintenance problem begins when a growing fintech responds to every new product, customer type, transaction pattern, and exception by adding more logic to the same monitoring layer.
Eventually, the organization is maintaining much more than individual rules. It is maintaining thresholds, dependencies, historical assumptions, testing processes, investigation workloads, product knowledge, data relationships, and governance around every change.
Scaling AML effectively therefore requires reusable risk context, stronger data foundations, historical testing, clear ownership, and monitoring workflows designed alongside the financial product itself. Rules can remain an important part of that architecture, but they should remain focused on the scenarios they handle well. Otherwise, the rule engine can gradually become the place where every new piece of product and compliance complexity accumulates.